MENU

AI agents increasingly need to authenticate, receive delegated authority, purchase services, and leave an attributable transaction record without human approval at every step. Identity sits underneath those interactions. It establishes who or what is acting, while scoped agent tokens define what that principal is authorized to do.
That separation matters as payment schemes diversify. A buyer may encounter x402, MPP, card-funded credits, stablecoins, or future agent ledgers, while a seller may want to monetize the same identity API across them. Identity lets buy-side and sell-side systems remain decoupled from any single settlement scheme. Identity platforms can then become agent-ready sellers, offering authentication, credential verification, resolution, and policy services that agents can purchase programmatically through Nevermined.
Agent identity provides a trust and attribution layer for autonomous interactions. It can help a service determine which principal is acting, which credentials belong to that principal, and whether the presented authority remains valid.
The W3C DID standard provides one model for persistent, verifiable decentralized identification. DIDs allow a controller to prove control over an identifier using cryptographic verification methods without relying on one centralized identity provider.
DIDs are one approach, not a requirement for every agent transaction.
Nevermined separates persistent identity from transaction authority. Its platform supports portable agent identity, while payment flows can rely on scoped credentials, smart accounts, and signed payment authorizations.
In an x402 flow, for example, an agent can receive a signed access token scoped to a payment plan and spending limit. That token represents authority for the commercial interaction rather than the agent's permanent identity.
The distinction is simple:
Identity establishes the principal.
The agent token establishes the scope.
For identity platforms, this creates a monetization opportunity. Authentication, credential verification, revocation checks, and identity management can become paid API operations that other agents purchase as needed.
Open agent identity efforts show how machine authentication can move beyond passwords and shared API keys.
Agent Identity (AID), for example, uses cryptographic identity and OAuth 2.0 token exchange so an agent can prove possession of its identity and obtain scoped credentials for API access.
Verifiable credentials can extend that model by carrying claims about an agent, organization, capability, or authorization.
An identity platform might verify whether an agent:
Those verification operations can themselves become monetizable services.
Identity platforms positioned as API providers can generate revenue from authentication, credential verification, identity lookup, revocation checks, and similar trust operations.
The x402 Facilitator can place payment verification and settlement around those API calls without requiring the identity platform to rebuild its authentication system as a billing system.
An identity platform might offer:
Each becomes a paid endpoint once pricing and access requirements are machine-readable.
With x402, an agent requests a protected endpoint, receives an HTTP 402 payment requirement, supplies payment authorization, and retries the request.
The identity platform still performs the verification.
The payment layer controls access to the paid service.
Prepaid credits provide another option for identity APIs that process many low-value requests.
A platform might sell a package covering a defined number of credential verifications. The buyer funds the balance once, then consumes credits as verification calls occur.
This separates funding from individual API consumption.
Nevermined's TypeScript and Python SDKs can handle payment validation, metering, and settlement around the service. The identity platform continues to define the credential format, verification logic, revocation rules, and trust model.
Agent-to-agent commerce requires authentication and authorization mechanisms that work for software acting without a human at the keyboard.
Authentication, access authority, and payment authority should remain distinct.
A principal may be authenticated but still lack permission to access a resource or spend money.
Nevermined security controls include FIDO2 passkeys and 3DS authentication for relevant enrollment and payment events.
Those controls can sit upstream of autonomous activity.
A human or organization establishes the payment method and delegates limited authority. The agent then operates inside that mandate rather than receiving unrestricted financial credentials.
For crypto-oriented settlement, structured signatures can also authorize defined payment terms without exposing the underlying private key.
The objective is scoped authority.
Not credential sharing.
Session keys provide one way to limit the authority held by autonomous software.
Instead of giving an agent permanent access to a root wallet or unrestricted credential, an operator can issue temporary authority with limits around:
If the task ends or the credential is compromised, that authority can expire or be revoked.
The CSA agent identity guidance similarly treats agent identity and access management as a lifecycle problem involving privileges, policy enforcement, and governance.
x402 standardizes a programmatic payment interaction around HTTP 402.
Identity is related to that interaction, but it is not the settlement rail itself.
An x402 transaction can carry payment-specific authorization while a separate identity layer provides continuity across transactions, services, and payment schemes.
Current x402 V2 also supports wallet-based identity and reusable-access patterns. It does not require every implementation to use one universal DID model.
Nevermined implements x402 across crypto and card-oriented payment paths.
For crypto flows, smart accounts can support stablecoin settlement. For card flows, delegated card authority can fund metered credits consumed as agent requests occur.
The seller's identity service does not need to depend on either rail.
A credential-verification API remains the same product whether the buyer settles through a stablecoin transaction or a card-funded balance.
The Machine Payments Protocol provides another HTTP-native model.
MPP uses payment challenges, credentials, and receipts. A service responds to an unpaid request with a payment challenge, the client fulfills it, and the client retries with a payment credential.
MPP is payment-method agnostic and can support both one-time charges and metered sessions.
It does not require DID-based identity.
An identity platform can still bind an MPP transaction to a persistent agent or organization, but that identity remains separate from the payment credential.
The layers are:
Identity: who is acting
Agent token: what authority the agent holds
Payment protocol: how buyer and seller communicate payment requirements
Settlement scheme: how value is transferred or accounted for
The AP2 protocol adds another authorization model through mandates represented as verifiable credentials. Identity and credential platforms can participate in verification around those flows depending on the trust architecture used.
Long-term interoperability depends on avoiding unnecessary coupling between identity, communication protocols, payment protocols, and settlement rails.
x402 and MPP are payment protocols.
A2A and MCP address other parts of agent interaction.
AP2 focuses on authorization and payment mandates.
These layers can work together without being treated as interchangeable standards.
A flexible architecture lets identity services remain useful while payment conventions change.
Nevermined supports x402 payment flows, while its Router can handle both x402 and MPP payment requirements on the buy side. It also provides integrations for agent interaction patterns such as A2A and MCP.
The broader goal is not to predict which standard will dominate.
It is to keep the identity provider's core service separate from that outcome.
A verification endpoint should not need to be rebuilt simply because the buyer changes payment protocols or a new agent ledger becomes available.
Identity platforms may need to support everything from individual verification calls to large enterprise authentication workloads.
Nevermined reports that Valory reduced deployment time for payment and billing infrastructure for the Olas AI agent marketplace from six weeks to six hours using its payment stack.
That is a customer-specific result rather than a universal integration benchmark.
For identity providers, the relevant point is architectural: payment, metering, and settlement can remain separate from the trust service itself.
The identity provider still defines the price of its own service.
Identity platforms have several options beyond a flat subscription.
The right model depends on the service being provided and which event can be measured reliably.
Usage-based pricing can charge per authentication, credential verification, revocation check, or identity lookup.
Outcome-based pricing can move the billable event closer to a successful result, such as a completed credential verification rather than every attempted request.
Transaction-linked pricing is also possible when the identity operation connects directly to a higher-value commercial workflow. That model requires stronger attribution between the identity service and the downstream event.
Different services can use different models.
Variable operational costs can also influence pricing.
A simple identity lookup may cost little, while advanced verification, external checks, or cryptographic proof generation may require more resources.
Payment model patterns can support usage, credits, dynamic pricing, and hybrid structures around those services.
Session-based consumption can also group several identity operations into one commercial unit.
For example, a workflow containing identity resolution, credential verification, and a policy check could be sold as one paid session.
The commercial model should follow what the buyer is purchasing rather than expose every internal operation by default.
Enterprise identity platforms need documented controls around authentication, credential handling, authorization, auditing, and payment security.
Using a compliant payment provider can support part of that requirement.
It does not replace the identity platform's own security responsibilities.
Nevermined maintains SOC 2 Type II, ISO 27001, and PCI SAQ-D controls for its payment infrastructure.
Its security documentation also describes tokenized card capture, scoped mandates, revocation, and transaction audit trails.
Those controls can help an identity provider document the payment layer during a security review.
They do not transfer Nevermined's certifications to the identity platform.
Identity security remains the provider's responsibility.
Privacy requirements depend on what identity data is stored, where it is stored, and how credentials or identifiers are linked to people or organizations.
DID deactivation or credential revocation can make a credential unusable, but it does not automatically erase personal information stored elsewhere.
Selective-disclosure and zero-knowledge techniques can reduce the information shared during verification when the credential system supports them.
Transaction and authentication logs can also support audits and reconciliation when retention and access policies are designed appropriately.
Identity gives buy-side and sell-side systems a common principal even when their payment infrastructure differs.
A buyer agent may hold a persistent identity plus temporary tokens representing a particular budget or task.
A seller may expose a paid identity service through x402, MPP, or another future payment interface.
The parties do not need to share the same internal account system.
They need interoperable ways to establish authority and satisfy the commercial requirement.
On the buy side:
On the sell side:
This separation enables agent-to-agent commerce without requiring every seller to onboard buyers into the same payment system.
The protocol can change.
The principal does not have to.
Nevermined can provide the commercial infrastructure around an existing identity or authentication API.
The identity platform remains responsible for:
Nevermined handles the payment side through pricing plans, scoped payment authority, metering, verification, and settlement.
For sellers, the identity API becomes an agent-ready service.
For buyers, scoped credentials and budgets define what an agent can purchase.
This keeps the layers distinct:
Identity provides continuity.
Agent tokens provide scoped authority.
Protocols such as x402 and MPP carry the payment interaction.
Settlement rails move or account for value.
That separation lets identity platforms monetize their own services without binding the product to one payment protocol or ledger.
Verifiable identity gives a system a persistent principal that can be authenticated across transactions. Scoped credentials or agent tokens can then define what that principal is authorized to access or purchase. Human operators can establish those boundaries in advance, allowing an agent to transact independently within them without making the identity itself equivalent to the payment credential.
The pricing mechanics can resemble other APIs, but the service being sold is a trust operation such as credential verification, identity resolution, authentication, revocation checking, or policy evaluation. Identity platforms can charge per call, per session, through credits, or through other measurable pricing models while keeping identity and authorization logic separate from payment.
Yes, but payment-layer compliance and identity-platform compliance should be evaluated separately. An identity provider can use payment infrastructure with established security certifications while retaining responsibility for its own authentication, credential management, privacy, and access controls.
They do not need to change the core identity product. If identity, payment authorization, and settlement remain separate, the same verification or authentication API can be sold through x402, MPP, or future payment schemes. The payment integration can evolve while the underlying billable identity service remains stable.
Nevermined can place pricing, payment authorization, agent tokens, metering, verification, and settlement around an existing identity API. The identity provider decides whether an agent or credential is valid. Nevermined handles the commercial interaction that gives an authorized buyer paid access to that service across supported payment protocols and settlement schemes.
See Nevermined
in Action
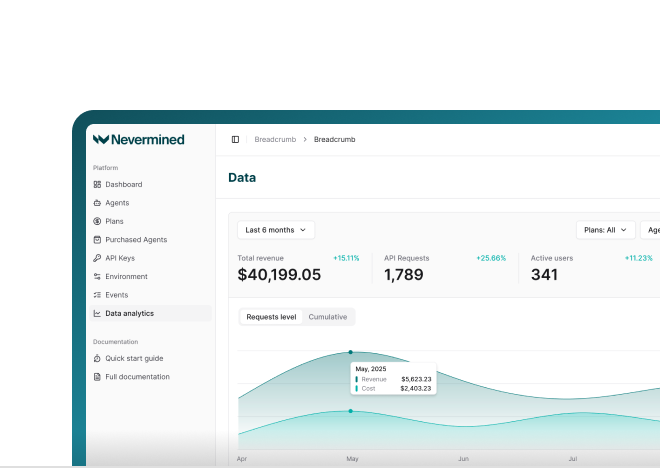
Real-time payments, flexible pricing, and outcome-based monetization—all in one platform.